 The security of the most widely used web CMS put to the test.
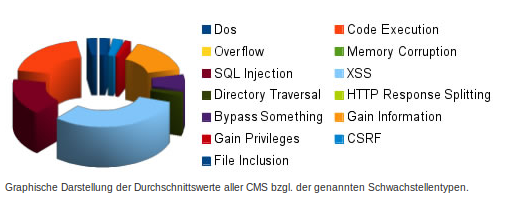
The Content Management Systems examined are: Drupal, Joomla!, Plone, TYPO3, and WordPress. The results are categorized into various attack methods, such as SQL injection or XSS (cross-site scripting).
In general, the study shows that the applications are quite secure and the manufacturers’ update processes are effective. Finally, the authors recommend adjusting the default configuration of the CMS used (e.g., changing the admin login) and implementing automated updates.